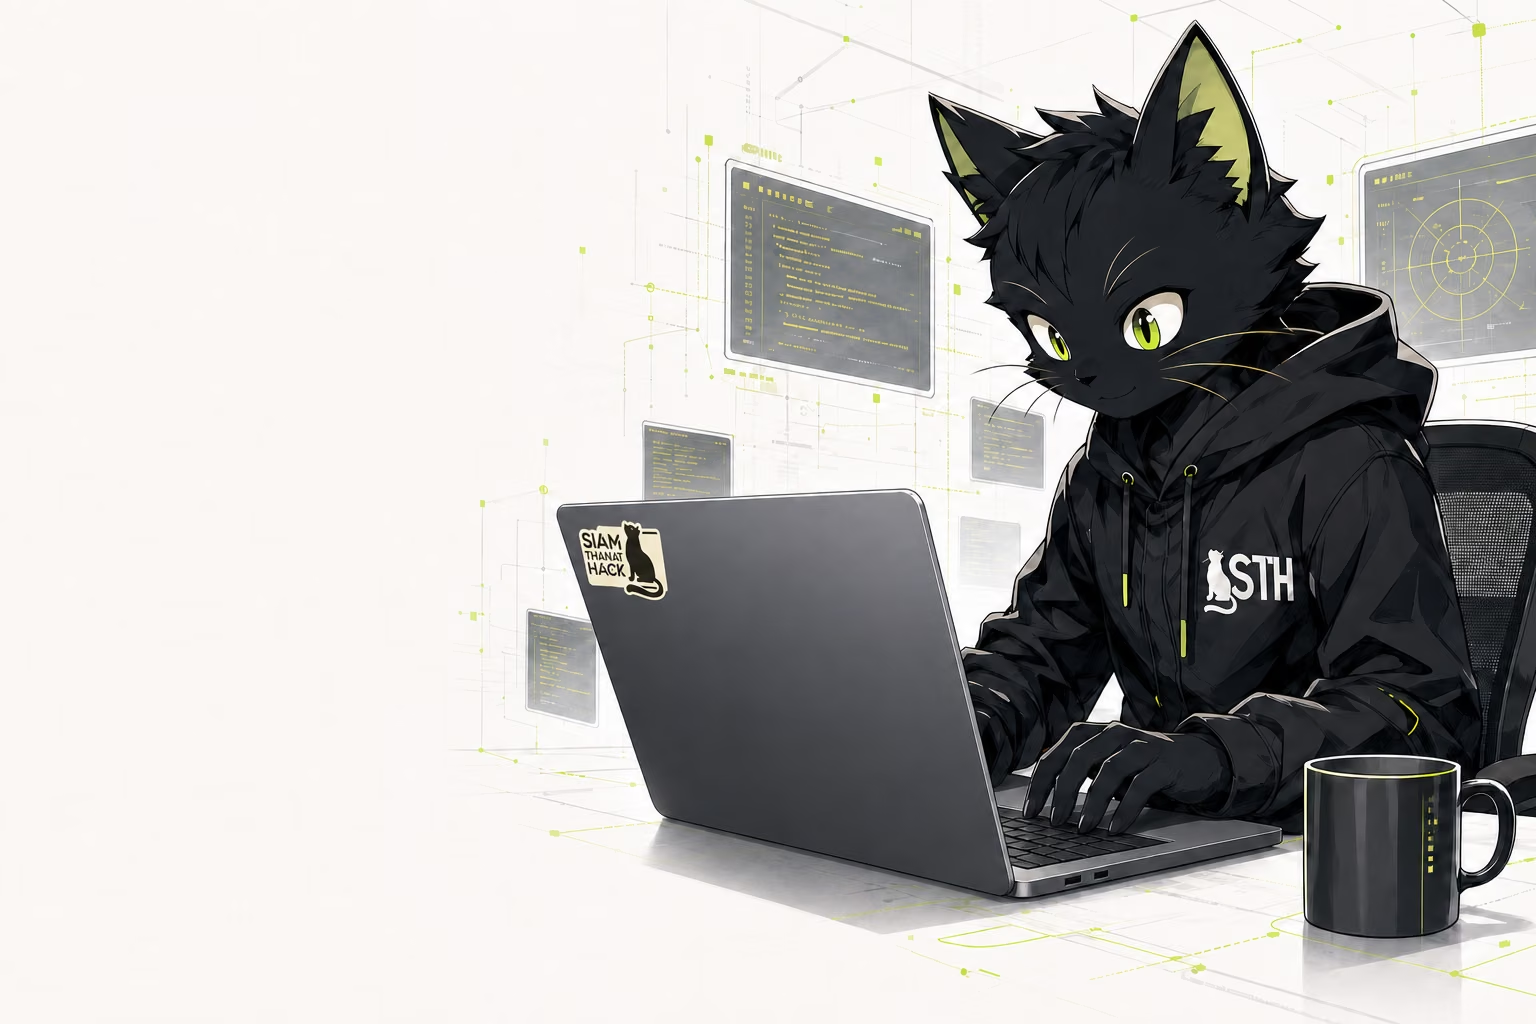
Japanese-style illustration of a young black-cat hacker testing a system on a MacBook Pro with an official Siam Thanat Hack sticker

Human-Led AI-Augmented

Professional penetration testing with the power of STH experts and AI

Penetration testing services for Web, Mobile, API, and Network with verifiable evidence and actionable remediation guidance

Siam Thanat Hack certifications

CREST Pathway Plus
Request a pentest quote Explore our services
Scroll to explore

OFFENSIVE SECURITY / 01

Our services

Find exploitable vulnerabilities with evidence and practical remediation.

01 / WEB APPLICATION PENETRATION TESTING

Go deeper than the OWASP Top 10

Test web applications for exploitable vulnerabilities, including business logic flaws scanners miss.

Coverage

  • OWASP Top 10 and OWASP ASVS
  • Authentication, sessions, and authorization
  • IDOR, injection, SSRF, and business logic

What you receive

Executive and technical reports with evidence, reproduction steps, impact, remediation, and scoped retesting.

02 / MOBILE APPLICATION PENETRATION TESTING

Covering both mobile applications and connected backend services

Test both the app and backend/API against the OWASP Mobile Top 10 to find exploitable vulnerabilities.

Coverage

  • On-device storage and encryption
  • TLS, certificate pinning, and sessions/tokens
  • Reverse engineering, tampering, and business logic

What you receive

Reporting and recommendations for both application and backend, a results briefing, and retesting within the agreed scope.

03 / API PENETRATION TESTING

Test every endpoint and chain realistic attack paths

Find authentication, authorization, rate-limiting, and data-exposure vulnerabilities in REST and GraphQL APIs.

Coverage

  • REST, GraphQL, and tokens/sessions
  • BOLA/IDOR, rate limits, and abuse
  • Mass assignment, data exposure, and business logic

What you receive

Endpoint-level reporting with evidence, reproduction steps, impact, and developer-ready recommendations.

04 / NETWORK PENETRATION TESTING

Validate attack paths from the perimeter to critical systems

Test external and internal networks within the mutually agreed scope and Rules of Engagement.

Coverage

  • Internet-facing services and VPN gateways
  • Internal networks, lateral movement, and Active Directory
  • Misconfiguration, privilege escalation, and segmentation

What you receive

Executive and technical reporting with network-segmentation evidence and scoped retesting.

05 / SECURE CODE REVIEW

Inspect logic beyond the reach of black-box tests and scanners

Manually analyze source code for vulnerabilities and logic flaws with practical remediation.

Coverage

  • Code-level authentication and authorization
  • Input validation, injection, and deserialization
  • Secrets, encryption, dependencies, and framework configuration

What you receive

Reporting with file/line locations, impact, fixes, and architectural guidance where needed.

06 / VULNERABILITY RESEARCH

Go deep into binaries, protocols, and exploitability

Research binaries, protocols, or codebases that require more than conventional checklist testing.

Coverage

  • Analyze specialized binaries, protocols, or codebases
  • Fuzzing, reverse engineering, and proof of concept
  • Assess impact and produce an advisory

What you receive

An advisory with proof of concept, risk prioritization, impact, and mitigation guidance.

Humans define scope and validate every finding. Within the authorized scope, AI runs automated active testing to increase speed, coverage, and efficiency against techniques real attackers may use.

ASSESSMENT GUIDE

VA Scan, Pentest and Red Team: which assessment do you need?

Each assessment answers a different question. Choose according to the objective, scope, and evidence you need; they are not automatic substitutes for one another.

Diagram comparing VA Scan, Pentest, and Red Team with an expert cat and AI robot for each assessment type

01 / VA SCAN

VA Scan / Vulnerability Assessment

Broadly discover and prioritize vulnerabilities. Scanner-only VA does not replace a Pentest.

Choose it when: You need an initial assessment of a large network environment, broad visibility of many vulnerabilities, and a plan for deeper validation.

02 / PENTEST

Pentest / Penetration Testing

Experts use manual testing to validate exploitability and impact within the agreed scope.

Choose it when: You need evidence that vulnerabilities are exploitable and remediation guidance for critical Web and Mobile applications.

03 / RED TEAM

Red Team

Simulate objective- and threat-led scenarios under explicit Scope and Rules of Engagement to assess prevention, detection, and response objectives.

Choose it when: You already run VA and Pentest regularly and need to test how people, processes, and technology respond to a defined scenario.

Scroll horizontally to view every column

VA Scan Pentest Red Team
Coverage
* Targets the stated objective, such as taking over a Domain Controller or implanting a backdoor while evading SOC detection, rather than seeking the greatest possible number of vulnerabilities.
Exploit proof
* Excludes vulnerabilities that could affect business continuity.
Real-world simulation
* Testing focuses on non-production systems to reduce impact.
* Focuses on testing detection and response processes.

Explore more articles and guides

ABOUT STH / 02

About

STH is a Thai white-hat team in Bangkok, combining deep expertise, operational discipline, and auditable communication.

Incorporated on 11 December 2018 with registered headquarters in Don Mueang and operational office near MRT Phra Ram 9, Bangkok.

01

Roots in knowledge sharing

STH grew from knowledge sharing. Former operators of the Facebook page Longhackz then expanded into CTF competitions, challenge creation, vulnerability research, and high-difficulty technical advisory work.

02

Experience with critical systems

Our specialists have worked on critical systems for banks, payment gateways, and leading organizations. We work strictly within an authorized scope and Rules of Engagement. We do not perform unauthorized access, account hacking, or account recovery.

03

Human-Led, AI-Augmented

Humans define scope and validate every finding. Within the authorized scope, AI runs automated active testing to increase speed, coverage, and efficiency against techniques real attackers may use.

Within the authorized scope, we use AI for reconnaissance and automated attack testing to explore the attack surface and test hypotheses faster. Specialists define scope, control testing, reproduce findings, assess impact, and approve the final report.

Professional certifications represented across the team

Passionate about offensive security and eager to grow with our team? Explore our open positions

HUMAN-LED × AI-AUGMENTED / 03

We test your systems from start to finish

Experts define scope, control testing, and validate results while AI runs automated active testing within scope to increase speed and coverage.

Human pentester, target system on phone and computer, and robotic-cat AI agent

Human owns the decision

Experts lead every step from scope to sign-off

  • Define scope, Rules of Engagement, and the test window
  • Model threats and find abuse cases scanners cannot see
  • Manually exploit and assemble attack chains
  • Assess impact, risk, and remediation before reporting

Evidence from the real surface

Test real system behavior, not just a checklist

  • Web, mobile, API, and network testing within the agreed scope
  • Assess access control, sessions, data exposure, and business logic
  • Capture reproducible evidence with clear impact explanations
  • Deliver remediation guidance development teams can apply

AI tests actively; humans retain authority

AI runs automated active testing; humans validate every finding

  • Perform reconnaissance and automated attack testing within the authorized scope
  • Build an evidence index and check coverage consistency
  • Assist with report drafting while every final report receives human review
  • An AI hypothesis never becomes a finding until a human reproduces it

DELIVERY FLOW / 04

Our delivery process

Every phase has a clear owner, evidence, and decision gate.

Phase 01 details

Plan

Turn business objectives into a clear, safe, and authorized testing scope before work begins.

Owner Engagement Lead Estimated duration 1-2 business days

What we do

  • Confirm in-scope and out-of-scope systems, domains, IP addresses, APIs, and applications
  • Prepare test accounts, access rights, MFA, and test data
  • Define the test window, Rules of Engagement, and stop conditions
  • Define communication channels and escalation procedures for critical events

Deliverables

  • Approved Scope & Rules of Engagement
  • Asset and Account Matrix
  • Test Schedule
  • Communication and Escalation Plan

Evidence

  • Testing authorization letter
  • System and endpoint inventory
  • Access Readiness Checklist
  • Contacts and approvers

Framework Mapping

Engagement GovernanceOWASP WSTG v4.2Authorized Testing

Decision Gate Begin testing only after scope, access, the test window, and ROE are fully confirmed.

View scope and ROE

Phase 02 details

Analyze

Build a threat model and attack-surface map to prioritize likely, high-impact attack paths.

Owner Lead Pentester / Security Analyst Estimated duration 1-3 business days

What we do

  • Analyze architecture, trust boundaries, and data flows
  • Build a threat model and abuse cases
  • Map the attack surface and exposed technologies
  • Analyze roles, privileges, and paths to sensitive data
  • Prioritize test scenarios by risk and impact

Deliverables

  • Attack Surface Map
  • Threat Model and Abuse Cases
  • Prioritized Test Scenarios
  • Initial Attack Hypotheses

Evidence

  • Endpoint and service inventory
  • Role and Privilege Matrix
  • Data flows and trust boundaries
  • Reconnaissance Artifacts

Framework Mapping

MITRE ATT&CK v19.2ReconnaissanceResource development - when authorized and in scopeOWASP WSTG: Information Gathering

Phase 03 details

Test

Perform authorized manual offensive testing to validate vulnerabilities and connect them into attack chains.

Owner Technical Lead / Pentest Team Estimated duration 5-15 business days

What we do

  • Test authentication, authorization, and session management
  • Analyze business logic and workflow bypasses
  • Validate vulnerabilities through manual exploitation
  • Connect multiple vulnerabilities to assess attack-chain impact
  • Keep testing within the Rules of Engagement

Deliverables

  • Verified Security Findings
  • Proof of Concept
  • Attack Chain Diagram
  • Test Coverage Matrix

Evidence

  • HTTP Requests and Responses
  • Screenshots and Screen Recordings
  • Commands, Logs and Tool Output
  • PoC code and impact evidence

Framework Mapping

OWASP Top 10:2025OWASP WSTG v4.2 Test IDsMITRE ATT&CK v19.2 Tactics & TechniquesOnly tested and validated behavior

Phase 04 details

Validate

Recheck results to remove false positives, define affected scope, and assess risk from proven evidence.

Owner Validation Lead / QA Reviewer Estimated duration 1-3 business days

What we do

  • Reproduce vulnerabilities under controlled conditions
  • Review attack preconditions and constraints
  • Use negative controls to distinguish expected behavior from vulnerabilities
  • Assess impact on confidentiality, integrity, and availability
  • Analyze business impact and real-world exploitability

Deliverables

  • Validated Findings
  • Affected Asset and Scope
  • Impact Analysis
  • Risk Rating and Rationale
  • Remediation Priority

Evidence

  • Reproduction Steps
  • Successful and Failed Test Cases
  • Privilege or data impact
  • Preconditions and Environmental Context

Framework Mapping

OWASP Top 10:2025 CategoryOWASP WSTG Test ReferenceMITRE ATT&CK Technique MappingImpact & Risk Validation

Decision Gate Classify results as Confirmed, Informational, or Rejected with traceable rationale.

View risk rationale

Phase 05 details

Report

Turn test results into prioritized, actionable information for executives and technical teams.

Owner Report Owner / QA Reviewer Estimated duration 3-5 business days

What we do

  • Summarize the overall risk and business impact
  • Document technical details and reproduction steps
  • Show attack paths and relationships between vulnerabilities
  • Recommend immediate and long-term remediation
  • Quality-review and remove unnecessary sensitive data from evidence

Deliverables

  • Executive Report
  • Technical Pentest Report
  • Finding and Evidence Register
  • Attack Chain Visualization
  • Prioritized Remediation Plan

Evidence

  • Sanitized Screenshots
  • Request and Response References
  • PoC and Reproduction Steps
  • Evidence Traceability Index

Framework Mapping

OWASP Top 10:2025 CoverageOWASP WSTG Test CoverageMITRE ATT&CK Attack PathFinding-to-Framework Matrix

Decision Gate Confirm facts, remediation owners, priorities, and items requiring retesting.

View report sample

Phase 06 details

Retest

Retest under the original conditions, check related bypasses or variants, and verify that risk is genuinely reduced.

Owner Original Tester / QA Reviewer Estimated duration 1-3 business days

What we do

  • Repeat the original PoC and test steps
  • Verify the root cause, not only the visible symptom
  • Test related variants and bypass paths
  • Check the fix for impact on existing functionality
  • Compare evidence before and after remediation

Deliverables

  • Retest Report
  • Finding Status Update
  • Closure Evidence
  • Residual Risk Summary
  • Outstanding vulnerability list

Evidence

  • Before and After Requests
  • Updated configuration or application version
  • Retest Screenshots
  • Timestamped Verification Results

Framework Mapping

Original OWASP Reference RetainedOriginal ATT&CK Mapping RetainedFix VerificationClosure Traceability

Decision Gate Confirm each post-retest status with evidence as Closed, Partially Remediated, Open, Unable to Verify, or Risk Accepted.

Timelines are estimates and may change with scope, access, and Rules of Engagement.

Governance & Compliance

Standards & Testing Frameworks

General & National Cybersecurity

Banking & Payment Systems (BOT)

Securities & Digital Assets (SEC) and Insurance (OIC)

VERIFIABLE TRUST / 05

Verifiable standards

Download our certificates and review the principles behind our delivery.

01

Human validation

Every finding is reproduced and manually validated

02

Evidence ready

Evidence, reproduction steps, impact, and remediation are included

03

Responsible AI

AI is an automated testing layer; humans decide the test results

04

Retest closure

Verify remediation and deliver evidence according to the package or scope

START THE CONVERSATION / 06

When you need a pentest,
work with specialists.

Send us your initial system details, testing scope, and preferred timeframe so we can prepare an assessment plan.

PENTEST FAQ / 07

Frequently asked questions about our Pentest services

Answers about scope, pricing, timelines, and regulatory requirements. If you cannot find what you need, talk to the team directly.

What is the difference between a Pentest and a VA Scan, and where should we start?

A VA Scan uses tools to discover vulnerabilities across a wide scope, which suits health-checking many systems and prioritizing risk first. A Pentest is hands-on testing by specialists to prove whether vulnerabilities are actually exploitable, with evidence and remediation guidance. Systems that are business-critical or hold customer data should get a Pentest alongside periodic VA, as one does not replace the other.

What expertise and certifications does the testing team hold?

The STH team has hands-on experience testing the applications of leading financial institutions and holds internationally recognized certifications at both the organizational level and the level of the individual specialists who run the tests, and were champions of Thailand Cyber Top Talent 2023. We support your engagement from start to finish: advising at the outset, preparing before testing, communicating vulnerabilities as they are found, and giving careful guidance on closing them.

Is the testing done by real people, or just an automated scanner?

Our work is human-led. Specialists define the scope, do the actual exploitation, and manually validate every finding before it reaches the report. We use AI and automated tools to speed up reconnaissance and widen coverage within the authorized scope, but the work a scanner cannot do, including chaining vulnerabilities into a real attack and testing business logic, IDOR, and authentication, stays with our experts. You get proof of real, exploitable impact with false positives already removed, not a ready-made scanner report.

How is Pentest pricing calculated?

Pricing follows the scope: how many systems, the size of each application, the number of functions or API endpoints to test, and the testing model (black-box, gray-box, or white-box). Send us your system details and the team will estimate the effort in man-days and issue a quotation with a clearly defined scope before any work begins.

How long does testing one system take?

It depends on the system's size and complexity. A single application typically takes about one to three weeks including reporting. After your team fixes the findings, we schedule a retest round to confirm the remediation.

What do we receive when testing is complete?

A full report with an executive summary and technical detail. Every finding includes reproduction steps, evidence, a CVSS-based risk rating, and practical remediation guidance. You also get direct access to the testers for questions, and a retest report after fixes.

Do regulators require penetration testing?

Several industries have direct requirements, including financial institutions under Bank of Thailand rules, securities and digital asset businesses under the Thai SEC, and card systems under PCI DSS. PDPA and the Cybersecurity Act define risk-based security duties instead. Some cite OWASP guidance directly, such as clause 6.2.2 of the Website Security Standard B.E. 2568 and Bank of Thailand notification SorNorChor 1/2564. We summarize each authority's requirements, with links to the source documents, at Regulations & standards

What do we need to prepare before testing starts?

Mainly, help us define the scope: the list of systems, URLs or app builds, test accounts for each user role, and the time window that suits you. We then prepare the scope and Rules of Engagement document for written sign-off before work begins.

How safe is our data during the engagement?

All testing happens within a written, authorized scope under a non-disclosure agreement. STH is certified to ISO/IEC 27001:2022 and ISO 9001:2015, which govern how evidence is handled, stored, and delivered throughout the project.

LEGAL & PRIVACY / 01

Privacy Policy

Last updated on July 13, 2026

We are committed to safeguarding and preserving the privacy of our website visitors. This policy explains how the website processes information and informs you of your rights regarding personal data.

Information Collected By Our Website

This website does not automatically collect personally identifiable information from visitors. Information submitted through the quotation form is used to assess project scope, prepare a proposal, and contact the requester under the consent they provide.

Cookies Used By Our Website

LINE Functionality

The third-party LINE widget is not loaded until you allow functional cookies. You can change or withdraw consent from Cookie settings in the footer. The first-party direct LINE link and QR code remain available without loading the widget.

Cloudflare Web Analytics

When you allow analytics cookies, the website loads Cloudflare Web Analytics to help us understand overall site usage. This script is not loaded when you choose essential cookies only, and you can change or withdraw consent from Cookie Settings in the footer. Read the Cloudflare Privacy Policy for details.

Site Optimization And Security

When deployed to production, we may use Cloudflare to optimize and protect the site. Cloudflare may process technical data or place cookies that are necessary to provide these services. Read the Cloudflare Privacy Policy for details.

Third Party Links

Our website may contain links to other websites. Once you leave our site, we do not control and cannot be responsible for how another website protects your information. Please review the privacy statement applicable to that website before providing information.

Changes To This Privacy Policy

We may update this Privacy Policy from time to time. The latest revision date appears at the top of this policy, and changes become effective when they are posted on this website.

Contact Information

If you have questions regarding this privacy policy, contact privacy@sth.sh.
QMS & ISMS / 02

Quality and Information Security Policy

Last updated on November 26, 2025

Siam Thanat Hack Co., Ltd. integrates quality management and information security into the core of our operations. We are dedicated to delivering precision-driven cybersecurity services while safeguarding the data entrusted to us.

Quality Policy (ISO 9001:2015)

We are committed to providing professional penetration testing and consultancy services that are accurate, actionable, and meet the highest professional standards. We adhere to the following principles:

  • Deliver evidence-based security assessments that allow clients to identify and remediate vulnerabilities effectively and precisely.
  • Consistently meet or exceed client expectations through timely delivery, clear communication, and expert consultation.
  • Ensure our technical team maintains industry-leading qualifications and continually updates its skills to match emerging technologies and attack vectors.
  • Continuously evaluate and refine our operational processes to maximize efficiency and service quality.

Information Security Policy (ISO/IEC 27001:2022)

We prioritize the protection of information assets belonging to our clients, partners, and our organization. We enforce controls to ensure the Confidentiality, Integrity, and Availability of data across all operations.

  • Rigorously protect intellectual property and sensitive data from unauthorized access, leakage, or tampering.
  • Proactively identify, evaluate, and mitigate security risks associated with our people, processes, and technology.
  • Operate in accordance with applicable laws, including the Personal Data Protection Act (PDPA), and relevant cybersecurity regulations.
  • Maintain robust incident response and business continuity plans to ensure resilience against security events.

Policy Communication & Review

This policy is communicated to employees and stakeholders to ensure a shared understanding of our standards. It is reviewed at least annually to remain aligned with our strategic direction and the evolving cybersecurity landscape.

Reporting Security Incidents

If you identify a security issue within our systems, report it directly to security@sth.sh. We acknowledge all security reports within 24 hours.

PROJECT INTAKE

Request a pentest quote

Share your systems, required services, and preferred timeframe so the STH team can assess the project and contact you.

01

Contact details

02 Services

03

Project Scope

04

Preferred service date